
Authentication and Authorization in Node.js

Authentication and authorisation are critical to building secure web applications. Here is an overview of both in Node.js:
Authentication:
Authentication is the process of verifying a user’s identity, making sure the user is who they claim to be. In a Node.js application, you can implement authentication using various strategies. Common strategies include:
-
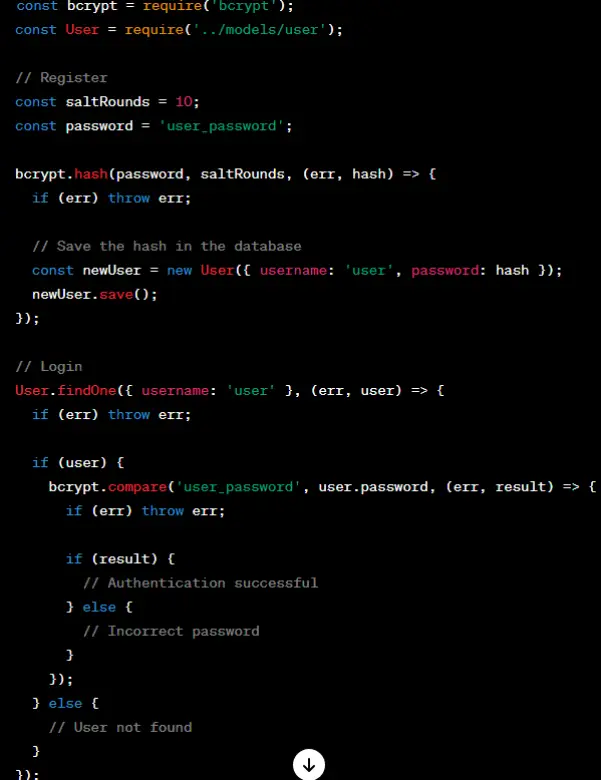
Username and Password:
- Use a library such as
bcryptto hash and store passwords securely. - Validate user credentials during the login process.
- Use a library such as
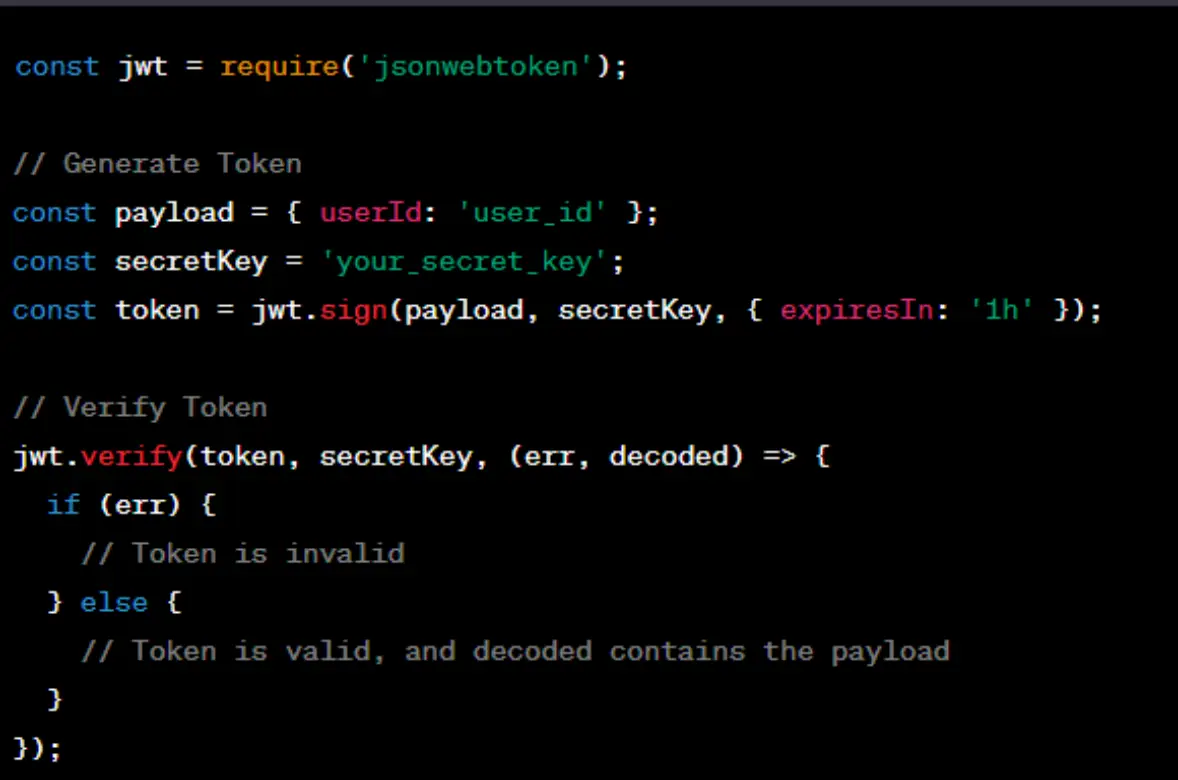
JSON Web Tokens (JWT):
- Generate a token after successful authentication.
- Include the token in subsequent requests for authentication.
Authorisation:
Authorisation determines what actions a user is allowed to perform in your application. After authentication, you can enforce authorisation using various techniques:
-
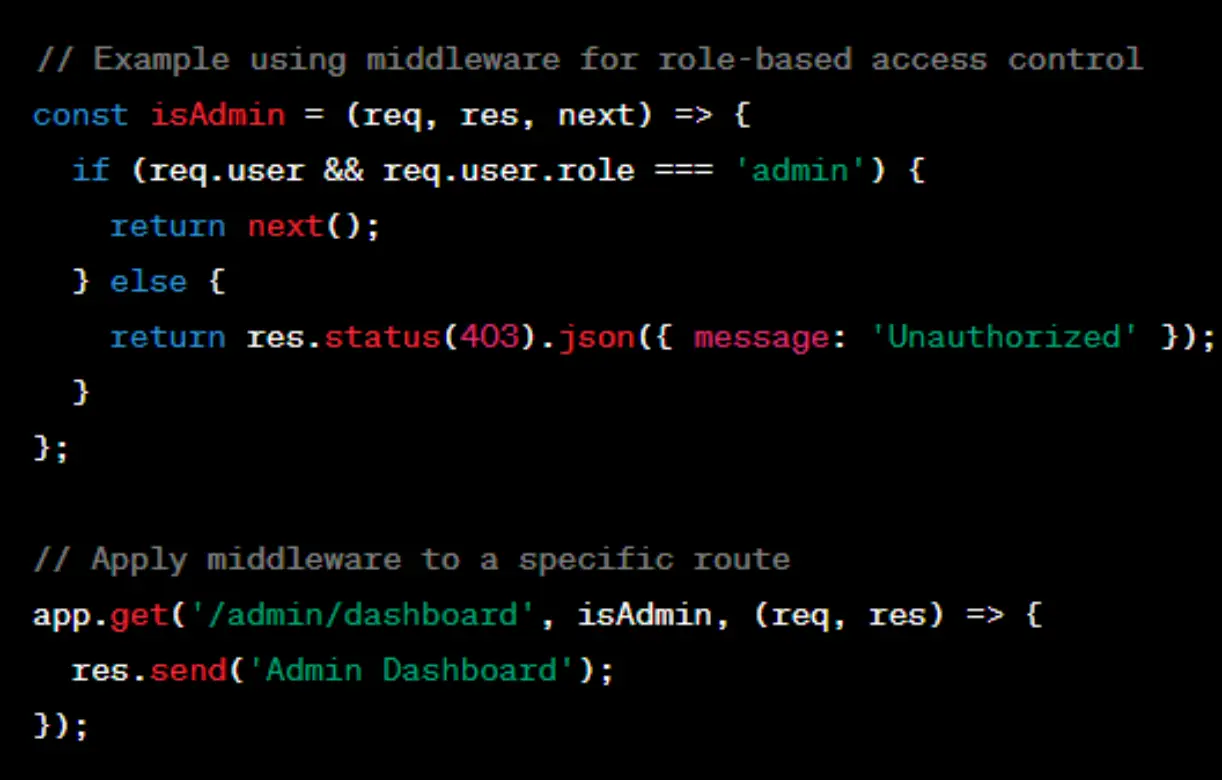
Role-Based Access Control (RBAC):
- Assign roles to users (for example, admin, user or guest).
- Define permissions based on roles.
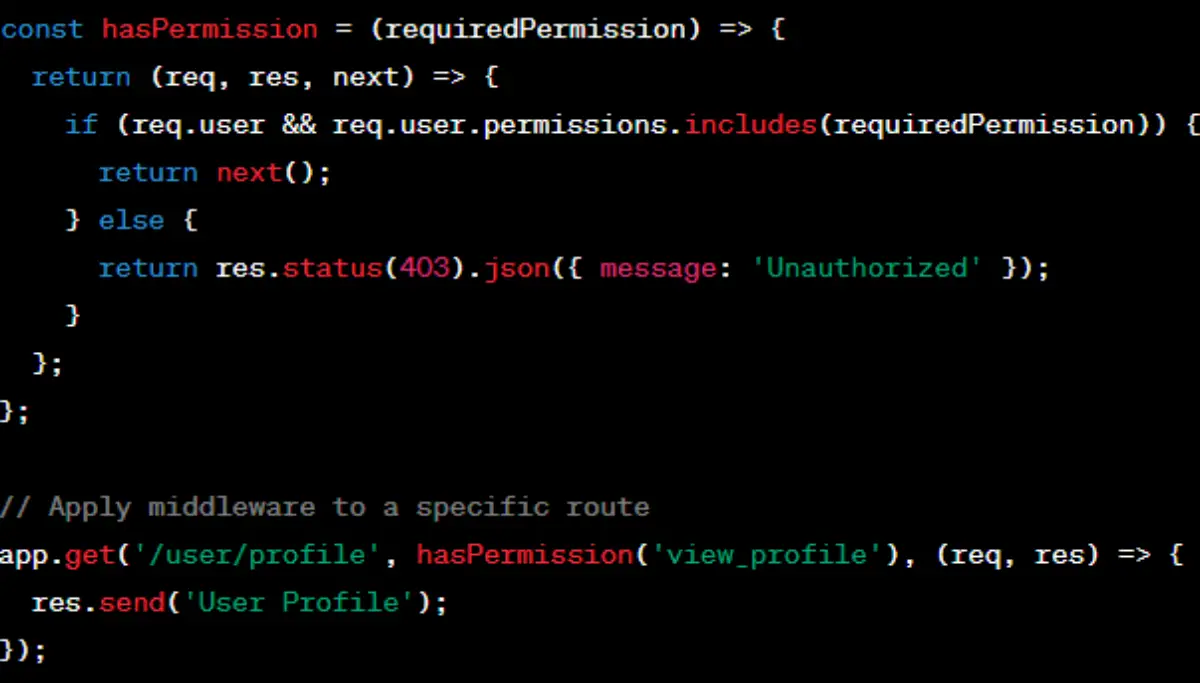
2. Middleware for Authorisation:
- Use middleware to check whether a user has the necessary permissions for a specific route.
3. OAuth and OAuth2:
- Delegate authentication and authorisation to external identity providers.
- Widely used for third-party sign-in with social or workplace accounts.
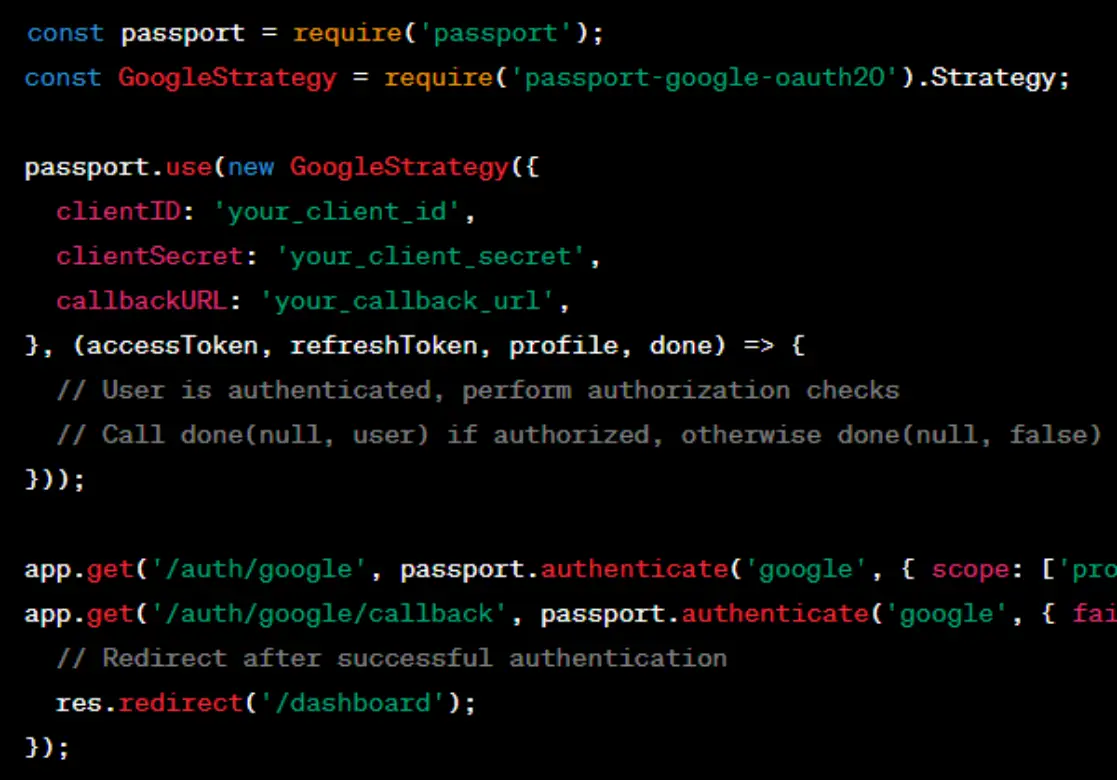
Tailor your authentication and authorisation strategies to your application’s specific requirements and security considerations. Consider using established libraries and frameworks, such as Passport.js, to simplify authentication and authorisation in your Node.js applications.
